AmbitiousProcess (they/them)

  • 0 Posts
  • 45 Comments
Joined 1 year ago
cake
Cake day: June 6th, 2025

help-circle
  • Using password login renders this vulnerability useless.

    This isn’t the case, though I can see how the article could lead you to believe that.

    It’s directly based on password rather than key input. The entire vulnerability is that typing a password longer than 256 characters automatically defaults to crypt() outputting the * character instead of a normal password hash, which is coincidentally the same default character used as the “hash” (not actually a value you could get from a normal hash, intended to be impossible to get from any normal password for that reason) for the built-in daemon account.

    When the Ars Technica article says “Second, the target system account must be configured to be passwordless”, what they mean is the default daemon account, which has a hash set to * by default, and thus wouldn’t normally be accessible via any hashed password… unless you happen to find out that the system chooses to not make a hash, and just send * if you type more than 256 characters.

    Look at https://sshhole.com/ if you want the details.


  • Maybe try Ente then?

    Haven’t used it before myself, but I’ve heard good things, and it does have a memories feature, and it seems at least based on the examples on their website that it might generate something more than just “today x years ago”.

    Unsure to what degree it works though, and unfortunately Ente is also a paid service (though it is privacy focused, and I believe it has a FOSS app too)

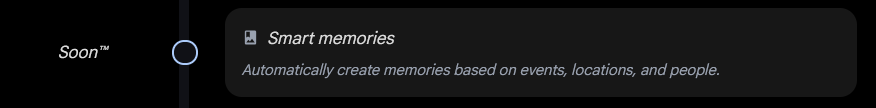
    Seems like “Smart Memories” are on the roadmap for Immich though, so you might just have to wait a bit and can then switch once they’re there:

    image

    There aren’t really any other mature options out there for self hosted, or even just private Google Photos alternatives in my experience, so you’re kinda just stuck with Immich for the most feature-complete replacement, and Ente for a more “just works” private but not self-hosted one. Everything else is basically just a glorified file browser, but maybe with some smart searching or better media codec support.


  • 100% Immich. Really good UI, and the kinds of quality of life features you don’t normally find in smaller open source apps (auto face tagging, map based on coordinates of photos, built-in non-destructive editor, memories, etc)

    The memories feature is mostly just “here’s photos/videos you took on this date”, but it doesn’t compile any sort of custom album based on a theme or place or anything like that. Not hard to do so yourself by just going to the map view and zooming into any location though.

    As for image searching it does have that, and I’ve found it to be shockingly reliable even when I run it on just a Raspberry Pi. (though it can take a while to give you the result of your search if you’re on lower-end hardware like that)


  • I would say if all you care about is having a nice looking, fully-featured, easy to use client, Proton is good, but if you really just need… an inbox with an email attached, then Tuta will be a little cheaper and just as private, just with less bells and whistles.

    If you care about removing yourself from other services like calendars, cloud storage, password managers, etc, Proton is way better since it has the full suite.

    For example, Proton supports auto-categorizing mail (e.g. newsletters, promotions, updates, transactions, etc), unlimited email aliases, a more modern UI, good integrations with Proton Drive and Proton Calendar if you decide to use those as well instead of Google Drive and Google Calendar, etc.

    Tuta is more just an inbox that you can bother to sort as needed, comes with some aliases if you feel like it but probably not enough for every single online service you have, has a basic calendar, but doesn’t have any kind of integrated Drive access (is still in closed beta rn), and has a more… basic UI.


  • I would be concerned about language collapse (i.e. models incrementally forget vocabulary + fail to adapt to new terms leading to language becoming incrementally worse) before I would worry about knowledge collapse

    Why so?

    The exact same mechanism is on display here. Ask an LLM for information, and it’s more likely to condense an answer, not display additional relevant information, and slowly but surely produce less and less outputs including that given information.

    Sources then begin to be generated by the AI model that adds less and less of that information over time, LLMs cite those new sources that don’t include that information, etc, etc, and now that information is just not present in a majority of sources, and is never stated in any LLM responses.

    If anything, this is more likely than models forgetting certain vocabulary, because while the underlying tokens for a lot of that vocabulary still exist in the model, the subsequent combinations for a given piece of information are substantially less likely, and the models’ finite size can only store a subset of that actual information in statistical averages. (i.e. you can store the alphabet and a dictionary of every word in the English language, and many simple phrases, in a tiny fraction of what the sum of Wikipedia is, and Wikipedia itself will contain a subset of all information on the internet, and so on, but you can still theoretically write any English content you’ll find on Wikipedia or the internet using that alphabet and dictionary)


  • all android devices have been using file based disk encryption since several Android versions now.

    All Android devices are supposed to support it, but not all do. (or at least, not all do effectively without compromising the cryptographic root of trust by not implementing proper hardware security chips)

    I’ll grant it to you on the scopes, PIN changes, etc, but realistically I just don’t think anyone can justify GrapheneOS being something that should be supported on Fairphone given how absolutely desolate the phone looks with regard to any attempt at all to hardware security.


  • It really depends on what security level you want out of a phone

    It does, but that’s exactly my point. GrapheneOS will provide you essentially no more security than any other alternative Android operating system, should it have to operate on a Fairphone with all those features not supported by a Fairphone stripped away.

    Unless Fairphone adds more hardware security features that are standard on most other phones, and highly supported on Pixels, installing a heavily crippled GrapheneOS on a Fairphone would get you essentially none of the benefits of GrapheneOS in the first place.


  • Entirely lacking disk encryption for typical users due to not having a secure element is a pretty major flaw.

    It’s also missing hardware accelerated virtualization which is necessary for much of GrapheneOS’s sandboxing, has weak security for other keys in the OS keystore, is missing hardware memory tagging which makes it much easier for apps to use overflow attacks, doesn’t have proper verified boot support once a custom alternative OS is flashed, and leaves exposed debugging APIs even when the phone is locked.

    This breaks:

    • Secure app spawning
    • Memory corruption protection
    • Integer overflow protection
    • Most of Graphene’s kernel hardening
    • Much of Graphene’s attack surface reduction abilities
    • Hardware-based attestation and security monitoring
    • Quick tile protection pre-unlock
    • Debugging access prevention
    • Verified Boot
    • The security of your PIN against any automated attack

    At that point, GrapheneOS can’t physically provide you essentially any security anymore.